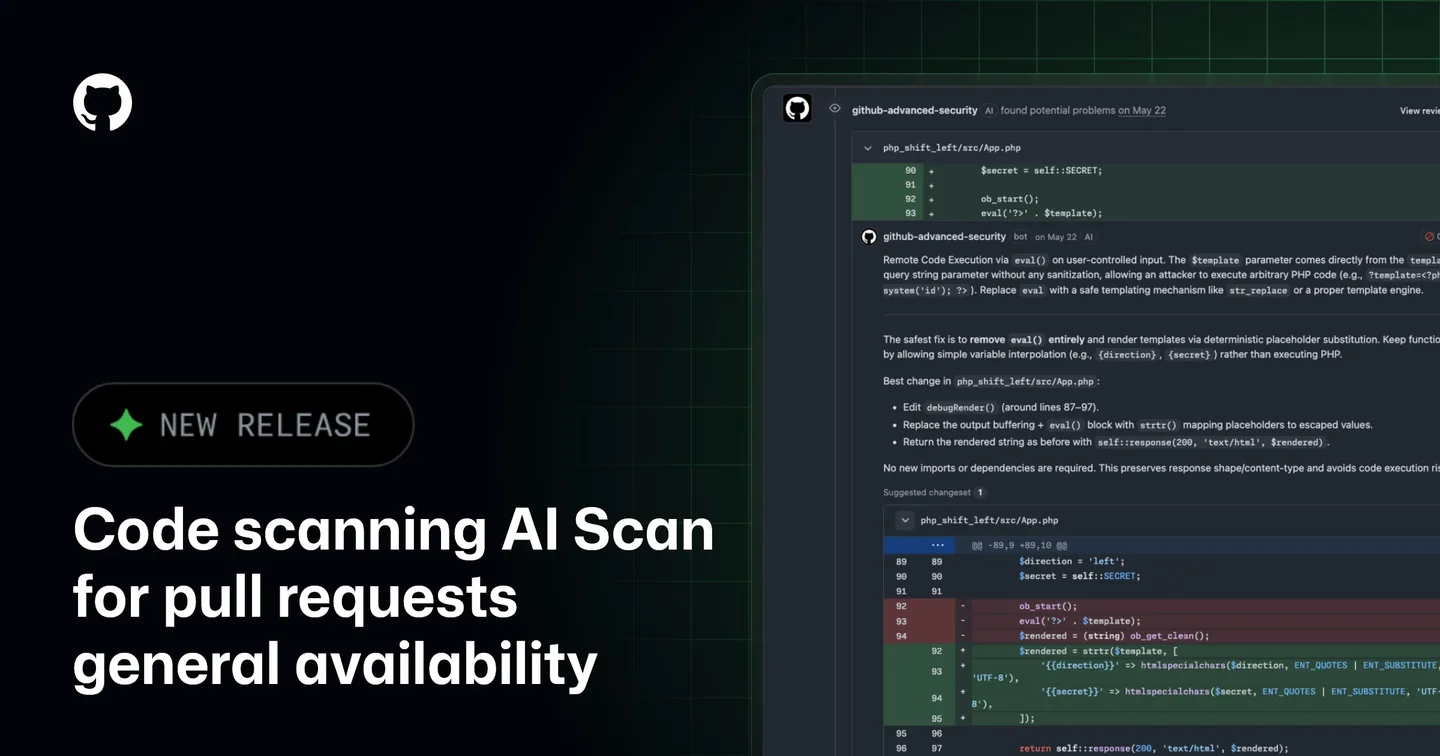
AI Scan adds advisory findings to pull requests alongside CodeQL, covering additional languages and formats such as PHP, Bash, Terraform and Dockerfile. Its October 15 general availability does not turn it into a merge gate: findings do not fail the scanning check and cannot block a merge through ruleset requirements. Pull requests from forks and Dependabot are outside its coverage.
Agentic autofix reaches general availability separately on the same day. It explores relevant repository files, proposes a correction, reruns CodeQL to check whether the alert closes, and opens a draft pull request for review. It can group up to 25 alerts from the default branch. A generated patch and a CodeQL rerun therefore remain part of a review process, rather than approval to merge automatically.
The access and cost boundaries are distinct. AI Scan is available for public repositories owned by organizations or individuals; private and internal organization repositories require GitHub Code Security or GitHub Advanced Security, not a Copilot license. Agentic autofix is available to Code Security and Advanced Security customers on GitHub Enterprise Cloud, including data-residency deployments. AI Scan consumes Code Security AI Credits, while agentic autofix also uses GitHub Actions minutes and requires appropriate administrator policies.
No independent product or account-access testing was performed for this entry. The sources do not specify a Belgian or EEA regional scope; account, contract and processing region still need to be considered. The announcements establish deeper integration of detection and remediation into the security pipeline, with human review and usage budgets still relevant.